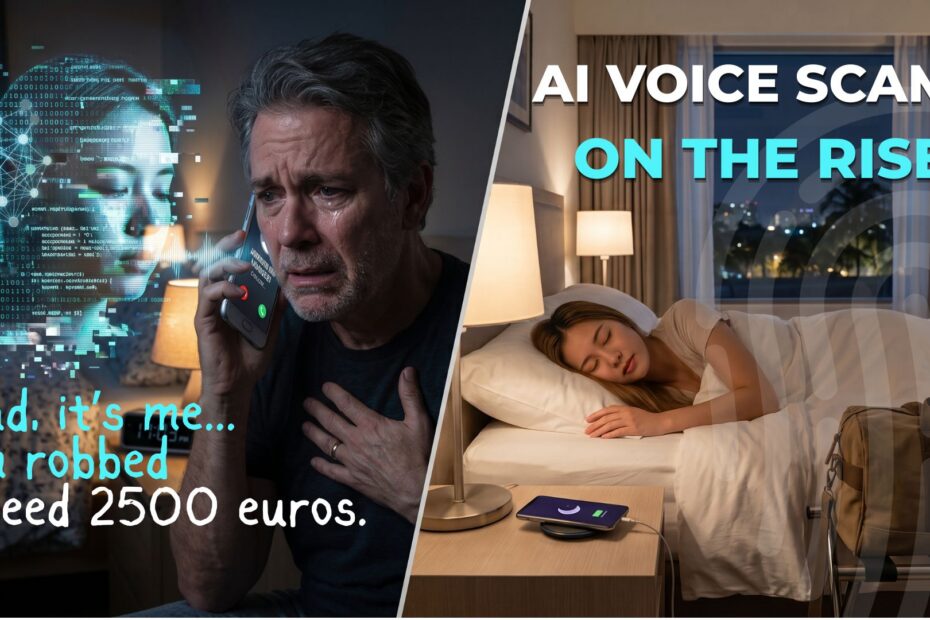
The phone rings at 11 p.m. It's your 19-year-old daughter's voice, calling from a number you don't recognize. Crying, frantic, saying they're stranded at a hostel somewhere in Southeast Asia. Their bag was stolen with their phone, passport, and cards inside, and the only reason they can call at all is a stranger lent them a phone. "Please, I need you to transfer €2,300 right now so I can pay for a new flight and a place to stay tonight, I'll explain everything after, please don't hang up." Every protective instinct you have fires at once.
Your daughter, meanwhile, is sleeping soundly in their hotel room on the other side of the world, phone charging on the nightstand (in do-not-disturb mode), bag never stolen, never on a borrowed phone to you at all. The voice on the phone was never theirs. It was a mathematically constructed copy of it.
This isn't a hypothetical scenario or a piece of speculative fiction. It's a documented, rapidly scaling criminal industry, and in 2026 it doesn't just target grandparents anymore. It also targets finance departments, executives, and anyone whose voice has ever been recorded and put online.
The Technology Got Cheap, Fast, and is Terrifyingly Good
Only a few years ago, cloning someone's voice took hours of clean studio audio and real technical skill. That barrier is gone. As cybersecurity nonprofit Operation Shamrock lays out in a detailed breakdown of the technology, modern voice-cloning tools need as little as three seconds of audio to produce a usable synthetic voice, and that audio doesn't need to be hard to find. Scammers can scrape it from Instagram Reels, TikToks, LinkedIn videos, YouTube clips, podcast appearances, or simply by calling your phone and letting your voicemail greeting play out.
The AI pipeline runs on a mix of open-source engines like ChatterboxAI, XTTS, and VALL-E, and commercial platforms such as ElevenLabs, which charges roughly $22 a month for its basic tier. These systems analyze hundreds of vocal characteristics, like pitch, pacing, nasal resonance, regional accent, and generate a synthetic voiceprint in seconds. The most advanced versions support real-time "voice skinning," where a scammer's live speech is converted into the cloned voice as they talk, letting them hold a fluid, improvised conversation instead of just playing a pre-recorded clip.
None of this requires elite hacking skills. Security researchers describe the criminal ecosystem behind it as a full "fraud-as-a-service" industry, complete with subscription pricing, feature updates, and customer support, built and sold the way legitimate SaaS products are.
The scale is already enormous. INTERPOL's 2026 Global Financial Fraud Threat Assessment found that automated, cyber-enabled fraud networks pulled in more than $442 billion in 2025 alone, that roughly one in ten adults worldwide has already encountered an AI voice scam, and that among people who engage with one, about a third lose money, an average of $18,000 per victim.
Your Colleagues' Voices: The New Business Email Compromise
If cloned family voices exploit love, cloned colleague voices exploit trust in workplace authority, and the euro amounts involved are staggering.
The reference case, now cited across nearly every security report on the topic, is the 2024 fraud against engineering firm Arup. A finance employee in Hong Kong joined what looked like a routine video call with the company's CFO and several colleagues, and authorized 15 separate wire transfers totaling $25.6 million. Every participant on that call except the victim was an AI-generated deepfake, voice and video both.
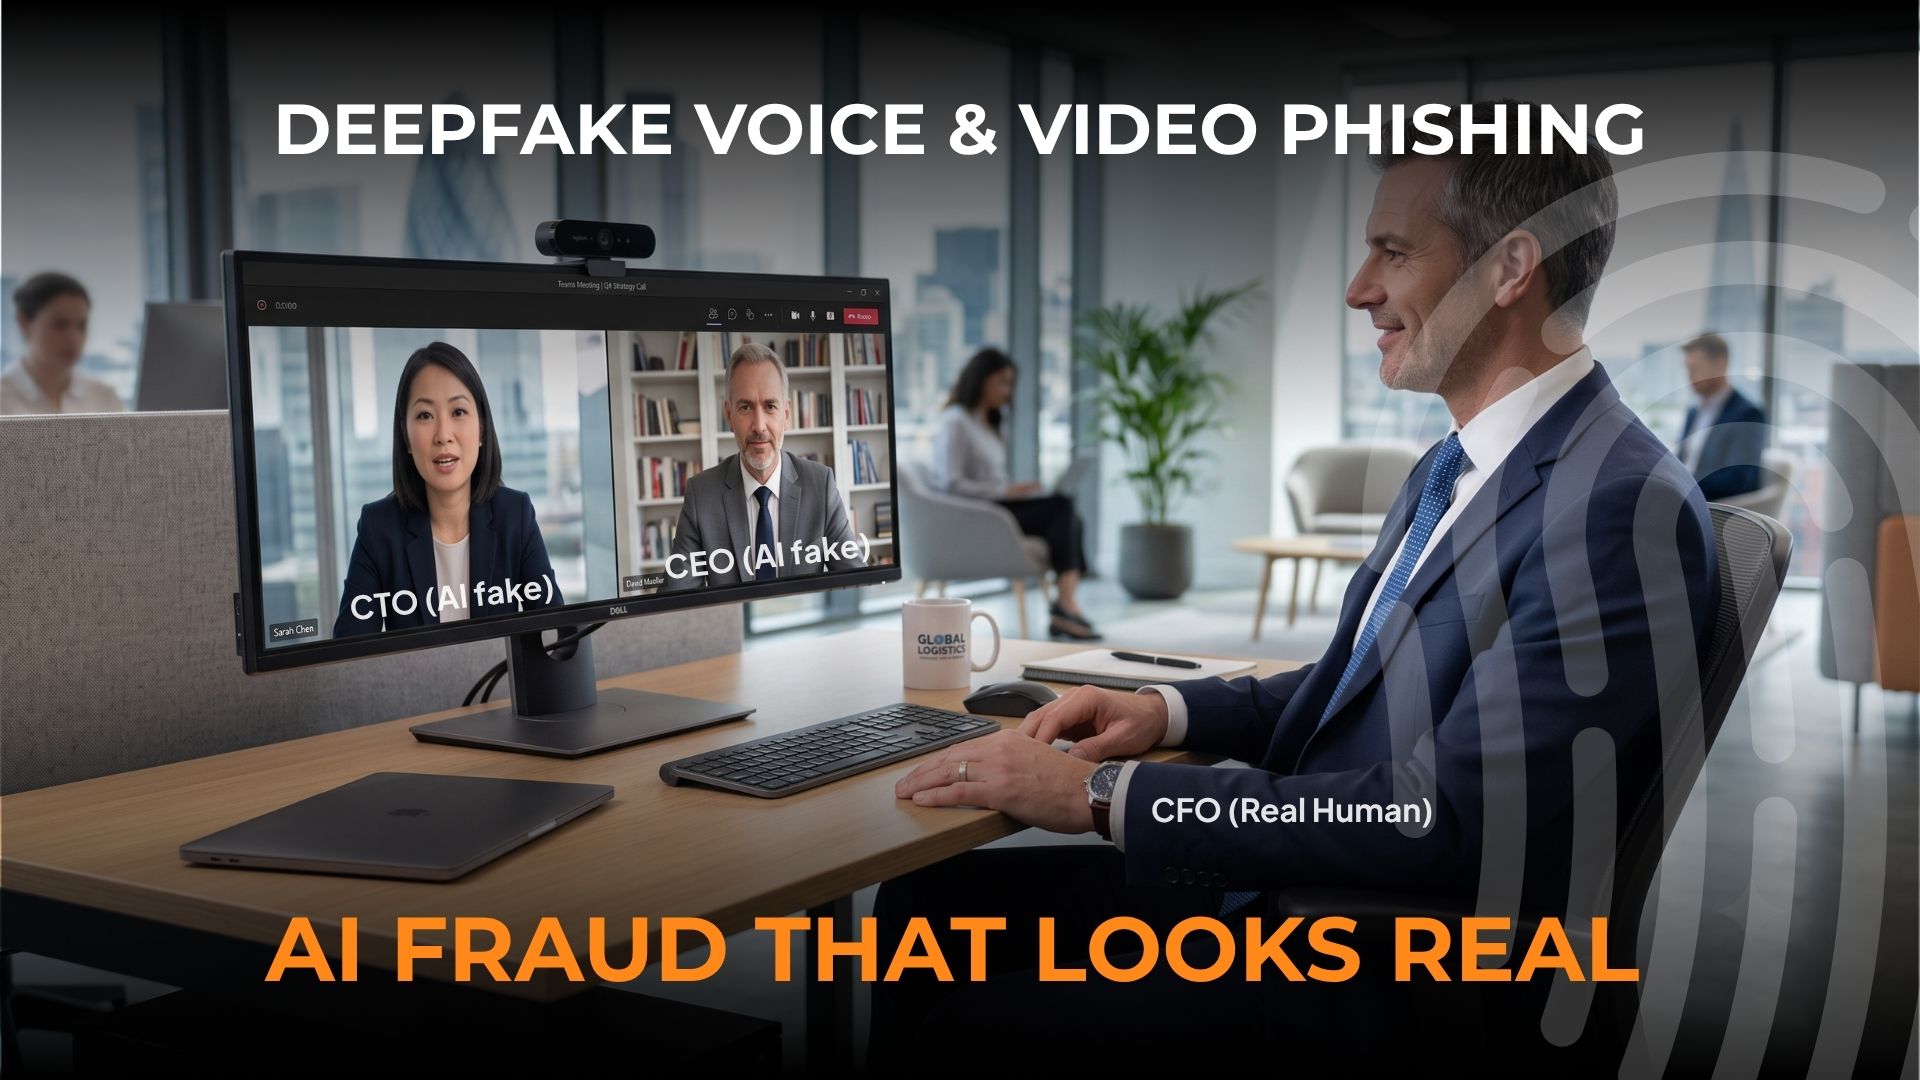
Security researchers describe this as the evolution of business email compromise (BEC), a fraud category that already cost businesses billions of dollars a year through spoofed emails and lookalike domains. The FBI's Internet Crime Complaint Center (IC3) attributed more than $4.6 billion in BEC losses in 2024, and multiple threat-tracking firms report that voice-deepfake-assisted BEC is the fastest-growing version of it. The typical attack chain looks like this:
The Typical Attack Chain in 4 Steps
This pattern isn't confined to giant engineering firms. In April 2026, the hacking group ShinyHunters used a vishing (voice-phishing) call to breach telecom provider Charter Communications, gaining access to an employee's account and, through it, roughly 4.9 million customer records. These are the steps they follow:
1. Reconnaissance: Scammers identify a company's owner, executives, and finance staff, then harvest voice samples from earnings calls, podcasts, conference talks, and LinkedIn videos. Thirty seconds of clean audio is often enough.
2. Setup: Attackers compromise or spoof a company email account, sometimes a real one obtained through credential theft, sometimes a lookalike domain that passes a casual glance.
3. Trigger: A cloned voice call arrives at a high-pressure moment, like payroll week, a closing deadline, a vendor payment cycle, instructing an employee to move money urgently and quietly, often with instructions not to loop in a second approver "yet."
4. Reinforcement: A follow-up email from the spoofed or compromised account backs up the verbal instruction, so the target feels they've "verified" the request through two channels when they've really just been hit twice by the same attacker.
In early 2025, criminals cloned the voice of Italy's Defense Minister and called high-profile business leaders claiming kidnapped journalists needed urgent ransom money; at least one victim wired nearly a million euros before police intervened.
And in early 2026, Swiss media reported a case in which an entrepreneur was talked into transferring several million francs over a series of calls, spread across two weeks, from a cloned voice impersonating a trusted business partner, a scam built not on panic but on patience.
Security researchers are blunt about why old defenses don't hold up anymore. Caller ID can be spoofed for a fraction of a cent per call. Email confirmation of a verbal instruction means nothing once the email account itself has been compromised. And the Arup case proved that even live video calls with multiple "participants" can be faked convincingly enough to defeat a trained employee who has no independent, out-of-band way to verify what they're seeing and hearing.
How to Protect Your Family and Business
Voice clones aren't undetectable, but the signs are getting subtler every few months. Researchers increasingly warn that unaided human listeners simply can't distinguish a good clone from a real voice anymore. That's why the recommended defenses have shifted away from "listen carefully for small tell-signs" toward hard, procedural rules that a voice clone can't talk its way around:
- Set a family code word. Choose something specific, memorable, and never written down, texted, or posted anywhere digital. If a caller claiming to be a loved one in distress can't produce it, treat the call as fraudulent.
- Hangup and call back on the known number. If a call feels wrong, hang up and dial the person's known number from your own contacts. Never redial, and never trust a number the caller gives you.
- Distrust unusual payment demands on principle. Hospitals, courts, law enforcement, and legitimate businesses do not ask for cryptocurrency, gift cards, or wire transfers as a condition of resolving an emergency. That request alone is close to a guaranteed scam signal.
- In workplaces, require dual authorization and out-of-band verification. No wire transfer above a set threshold should move on a single verbal instruction, however senior the "voice" on the call sounds. A callback to a known number, plus confirmation through a separate channel like an internal chat tool, should be a hard requirement, not a courtesy.
- Run the drill before you need it. Security teams increasingly recommend quarterly tabletop exercises where someone plays the role of a fake CEO calling the finance department, so employees build the habit of verifying under pressure rather than improvising it during a real attack.
Some longer-term technical defenses are also emerging. STIR/SHAKEN call authentication, a legal requirement for US carriers since September 2025, digitally signs calls so carriers can better verify caller ID.
Upcoming Standards like C2PA and watermarking systems such as Google's SynthID aim to cryptographically flag AI-generated media at the source. Forensic tools used by investigators can analyze raw, uncompressed audio for the algorithmic fingerprints a clone leaves behind, though that only helps after the fact, and only if the original audio wasn't compressed by a messaging app first.
Every Business Should Have an Automated Human Awareness Training Program. Contact SecWise.
As cybercriminals increasingly target people through phishing, vishing, and AI-powered social engineering, continuous employee education is essential. People need to be aware all the time.
SecWise helps organizations build a strong human firewall through automated phishing simulations, awareness training, and measurable security coaching.
 We use cookies on our website to give you the most relevant experience by remembering your preferences and repeat visits. By clicking “Accept All”, you consent to the use of ALL the cookies. However, you may visit "Cookie Settings" to provide a controlled consent or reject all cookies by clicking "Reject All".
